When integrations are handled as separate development projects, engineering teams often repeat the same work: mapping data fields, implementing authentication, managing API errors, testing callbacks and resolving inconsistencies between systems. The result can be longer delivery cycles, higher maintenance costs and more opportunities for production issues.
These are some of the most common iGaming integration challenges facing operators as their technology ecosystems expand.
The important point is that faster integration should not mean weaker testing or less operational control. Operators need a repeatable integration process that makes new connections easier to deliver while preserving transaction accuracy, security, platform availability and compliance.
This guide explains how to achieve that through reusable integration layers, API standards, sandbox testing, webhook reliability, reconciliation and controlled deployments.
Why Do iGaming Integrations Take So Long?
An iGaming platform typically connects multiple systems, each with its own technical specifications and business logic. A game provider may use a different session model from another studio. Payment gateways may return different transaction statuses. Verification services may use different data formats and response structures.
Even when two providers offer similar functionality, their interfaces may behave differently.
Common sources of delay include:
- Inconsistent API specifications and authentication methods
- Different player, transaction and session identifiers
- Incomplete or unreliable sandbox environments
- Delayed provider responses and technical documentation
- Unclear ownership of integration requirements
- Webhook delivery failures and duplicate events
- Manual testing and repetitive certification procedures
- Inadequate transaction reconciliation
- Production changes without sufficient rollback controls
These problems are not always caused by poor development. Integration delays can also result from missing documentation, external provider dependencies, unclear commercial decisions or regulatory approval processes.
The solution is to make integration delivery a defined engineering capability rather than treating every new supplier connection as an entirely new project.
1. Build a Reusable Integration Layer
One of the most effective ways to reduce repeated integration work is to introduce a reusable integration layer between the core platform and external providers.
Without this layer, the platform may need separate custom logic for every game provider, payment gateway or external service. As the number of integrations increases, the engineering team must maintain more individual connections.
A reusable layer provides a consistent internal interface while handling provider-specific differences behind it.
How does a reusable integration layer work?
Consider an operator connecting three different payment providers.
Each provider may have its own:
- Authentication method
- Deposit and withdrawal endpoints
- Transaction status codes
- Currency and amount formats
- Callback structure
- Error responses
- Refund and cancellation procedures
Instead of allowing each provider's unique structure to spread throughout the platform, the integration layer translates external requests and responses into a standard internal format.
For example:
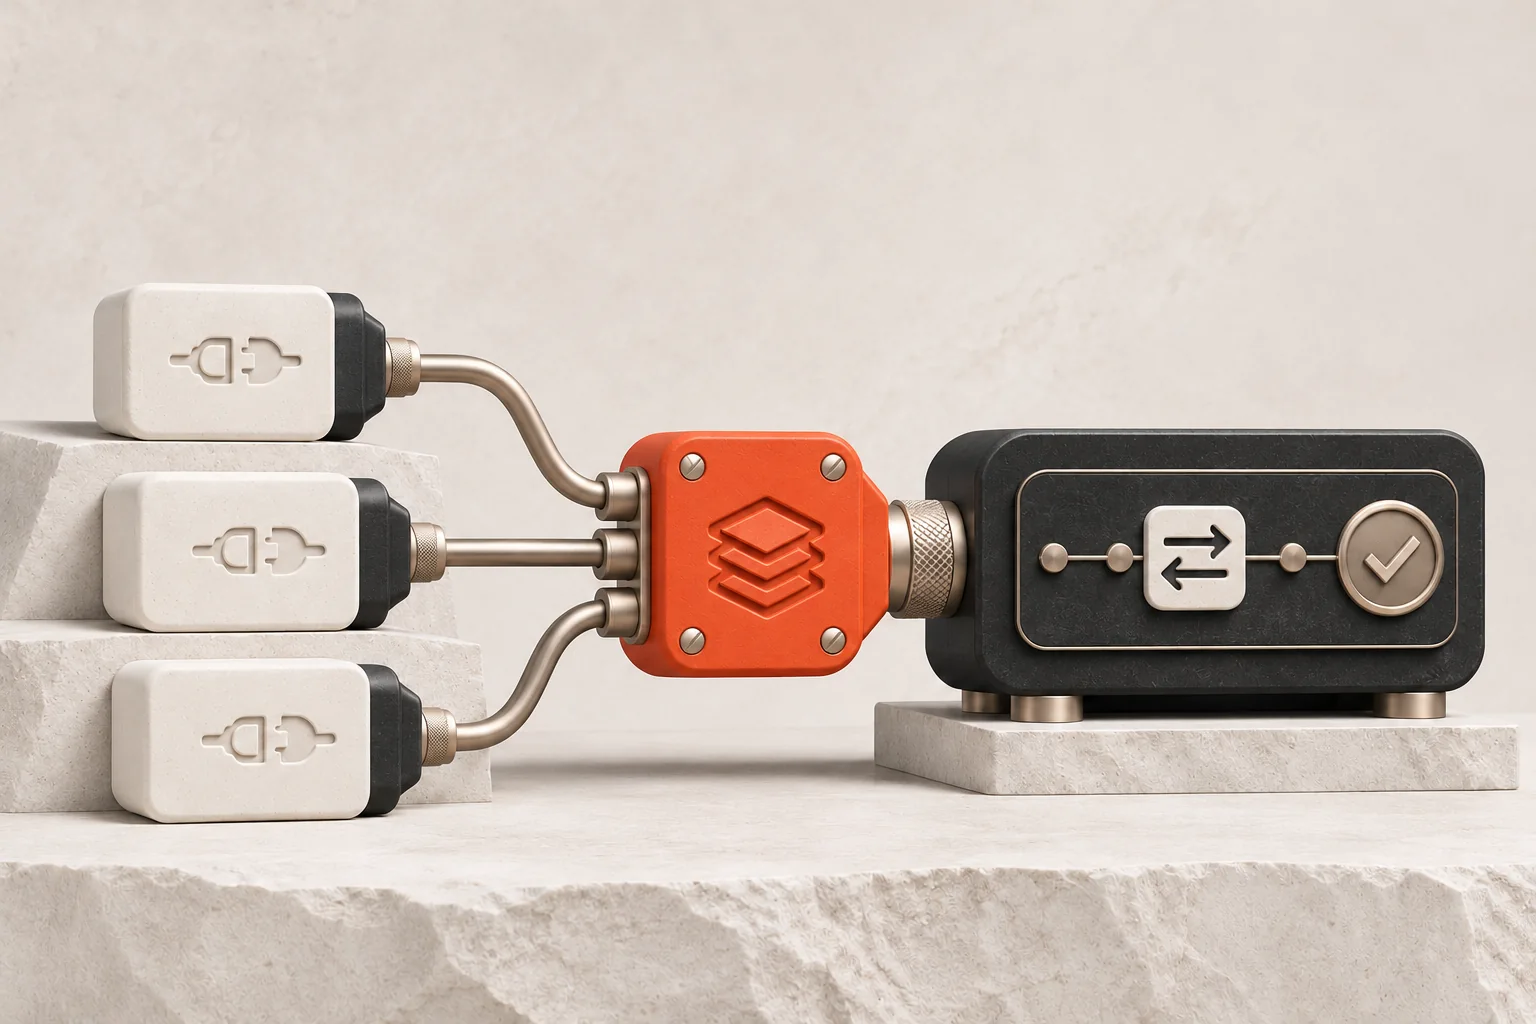
External payment providers → Provider-specific adapters → Shared integration layer → Internal wallet and payment services
The wallet service interacts with a consistent internal contract. Each adapter handles the differences between the external provider and that contract.
The same architectural principle can be applied to game providers, KYC services, CRM systems and other integrations.
What should the integration layer include?
A practical implementation may contain:
Provider adapters: Separate connectors that handle supplier-specific endpoints, authentication and data formats.
Common data models: Standard definitions for players, sessions, transactions, currencies and event statuses.
Authentication management: A consistent method for managing credentials, tokens, permissions and provider access.
Error handling: Standardised treatment of timeouts, invalid responses, rejected requests and temporary provider failures.
Logging and monitoring: Shared visibility into requests, responses, processing times and integration errors.
Configuration management: Provider-specific settings maintained separately from core business logic.
Why does this reduce delivery time?
The team can reuse established components rather than rebuilding common functionality. A new provider still requires implementation and testing, but the work becomes more focused on its unique requirements.
The integration layer also makes future maintenance easier. If an external provider changes its API, the team can often update the corresponding adapter without modifying unrelated platform services.
Important: A reusable layer should not hide meaningful differences between providers. Payment settlement rules, game-round behaviour and compliance requirements must remain explicit. Standardisation should simplify technical connections without weakening business controls.

2. Define API Standards Before Starting Integration
API inconsistencies are a major source of development rework. If internal teams use different naming conventions, authentication methods, error formats and transaction structures, each new connection becomes harder to understand and maintain.
A documented API standard gives internal developers and external suppliers a shared technical reference.
Establish a common API contract
An API contract should explain how systems communicate and what each side is responsible for.
Important areas include:
API standard | What to define |
|---|---|
Authentication | Token types, credential handling, permissions and expiry |
Data formats | Field names, data types, required values and response structures |
Identifiers | Player IDs, transaction IDs, session IDs and provider references |
Error handling | Standard error codes, retryable failures and rejection reasons |
Versioning | Version policy, backward compatibility and deprecation timelines |
Time and currency | Timestamp formats, time zones, currency codes and decimal precision |
Request limits | Rate limits, timeouts and expected response behaviour |
Security | Encryption, request validation and access permissions |
Use consistent transaction states
One provider might use SUCCESS, another might use COMPLETED, while a third might return a numerical status.
The platform should map these external values into a clearly documented internal state model.
For example:
- Pending
- Processing
- Completed
- Failed
- Cancelled
- Reversed
The exact state model depends on the business process. A payment marked as pending should not be treated as completed simply because the external response contains a successful HTTP status.
Define API ownership
Every interface should have an owner responsible for its documentation, changes, testing and operational performance.
A shared contract should also define how suppliers communicate breaking changes and how much notice they must provide.
Standards reduce ambiguity, but they do not eliminate the need for provider-specific testing. A technically valid response can still produce an incorrect business outcome if the underlying transaction logic is misunderstood.
3. Use Sandbox Testing to Identify Problems Before Production
A sandbox allows developers to test an integration without exposing live players, financial transactions or production services to unnecessary risk.
However, simply receiving a test API key does not mean the sandbox is sufficient. Testing environments vary significantly in their available scenarios, data and behaviour.
A useful sandbox should support realistic testing of both normal and exceptional situations.
What should operators test?
Authentication: Confirm that valid credentials work, expired credentials are rejected and unauthorised requests cannot access protected resources.
Successful transactions: Test the expected flow for deposits, withdrawals, game launches or other relevant operations.
Failed transactions: Check how the integration responds to insufficient funds, rejected requests, invalid parameters and provider errors.
Timeouts: Simulate a delayed response or unavailable provider to ensure the platform does not incorrectly assume that a transaction failed or succeeded.
Duplicate requests: Submit repeated requests and verify that they do not create duplicate financial or business events.
Session handling: Test session creation, expiration, reconnection and termination where relevant.
Currency and precision: Validate supported currencies, decimal handling, conversion rules and rounding behaviour.
Webhook delivery: Test delayed, repeated, malformed and out-of-order callbacks.
Build automated integration tests
Manual testing is useful during initial development, but it becomes inefficient when an operator has many providers to maintain.
Create reusable automated test suites for common scenarios. Run them whenever an adapter, API contract or provider integration changes.
Contract testing is particularly valuable. It verifies that the provider and platform continue to follow their agreed interface, helping teams identify breaking changes before they reach production.
A staging environment should also resemble production in important ways, including configuration, service dependencies, security controls and expected data volumes.
A sandbox should reduce uncertainty, not create false confidence. If the provider's test environment does not reproduce important production behaviours, document those limitations and add additional controlled testing before launch.
4. Make Webhook Delivery Reliable
Many iGaming integrations depend on webhooks to communicate events between systems.
A payment gateway may notify the platform that a deposit has been completed. A game provider may send round results or session updates. A verification service may communicate the outcome of an identity check.
Webhooks allow systems to communicate events without requiring constant polling. However, they also introduce reliability challenges.
A callback may arrive late, arrive more than once, arrive out of order or fail to reach the receiving system.
Common webhook problems
- The receiving service is temporarily unavailable.
- A network interruption prevents delivery.
- A provider sends the same event repeatedly.
- The callback arrives before another related event.
- The receiving system processes the event but fails to acknowledge it.
- The provider retries an event that has already been completed.
Without appropriate handling, these issues can cause inconsistent records or duplicate actions.
Recommended webhook reliability controls
Verify webhook authenticity: Validate signatures or the provider's documented authentication mechanism before processing incoming events.
Use unique event identifiers: Store a stable reference for every incoming event. This allows the platform to recognise previously processed notifications.
Implement idempotency: Processing the same event more than once should not create an additional deposit, withdrawal or other unintended business action.
Acknowledge appropriately: Return the expected response only after the event has been safely accepted for processing. Avoid lengthy business operations inside the callback request.
Use retry policies: Retry temporary failures with controlled backoff. Avoid endless retries or aggressive retry loops that can overload services.
Maintain a dead-letter queue: Store events that cannot be processed after the defined retry process. Make them available for investigation and controlled reprocessing.
Handle event ordering: Where the provider does not guarantee delivery order, use transaction states, timestamps and authoritative source records to determine the correct processing sequence.
Monitor webhook health: Track delivery delays, failed callbacks, retry counts, duplicate events and unresolved messages.
A reliable webhook system should make event delivery observable and recoverable. It should never depend on the assumption that every callback will arrive exactly once and in the correct order.
5. Implement Transaction Reconciliation
An integration is not complete simply because the API returns successful responses. The platform must also ensure that the resulting business records are correct.
This is especially important for payment and wallet integrations.
For example, a payment provider may record a deposit as completed while the platform wallet remains unchanged because an internal processing step failed. The opposite problem is also possible: the platform may credit an account before receiving the authoritative payment confirmation.
Reconciliation helps identify and resolve these inconsistencies.
What should be reconciled?
Depending on the integration, operators may need to compare:
- Payment provider transaction records
- Internal wallet ledger entries
- Deposit and withdrawal statuses
- Refunds and chargebacks
- Game-round and settlement records
- Provider references and internal transaction IDs
- Currency amounts and conversion calculations
Build a structured reconciliation process
1. Match records: Use stable identifiers to connect external provider transactions with internal records.
2. Compare values: Validate amounts, currencies, transaction statuses and relevant timestamps.
3. Identify exceptions: Detect missing records, duplicate entries, mismatched amounts and inconsistent states.
4. Assign ownership: Route each discrepancy to the appropriate finance, operations or technical team.
5. Resolve and record: Document the investigation, correction and supporting evidence.
6. Reconcile again: Confirm that the corrected records now match the authoritative source.
Automated reconciliation can reduce manual effort, but exceptions still require appropriate investigation and approval.
For payment integrations, this process is particularly important because a technically successful connection does not guarantee financial accuracy.
6. Use Controlled Deployment Instead of Releasing Every Integration at Once
A completed integration should not automatically be enabled for every player, market or transaction type.
A controlled deployment process allows operators to observe how a new connection behaves before exposing the entire platform to it.
Recommended deployment controls
Feature flags: Keep a new integration disabled until the required checks are complete. Feature flags can also support controlled activation and rollback.
Limited rollout: Where the architecture and business rules permit, introduce the integration to a limited market, product or controlled user group before expanding access.
Health checks: Monitor API response times, error rates, webhook failures, transaction statuses and provider availability.
Rollback procedures: Define how to disable the integration or restore the previous configuration without damaging existing transaction records.
Configuration validation: Check credentials, endpoint URLs, currency settings, market restrictions and other production parameters before activation.
Approval workflows: Require appropriate technical, operational and compliance approval before enabling sensitive integrations.
Release documentation: Record the version deployed, configuration changes, test evidence, approvals and recovery steps.
For larger platform changes, techniques such as blue-green deployment or canary releases may reduce exposure to deployment problems. The correct approach depends on the architecture and whether the integration supports safe traffic switching.
A rollback must not erase completed transactions or reverse legitimate financial activity. Financial state recovery should follow a separate, auditable process.

7. Treat Security and Compliance as Part of Integration Design
Speed should never come from skipping security or compliance requirements.
Every external connection introduces a new trust boundary. A payment provider, game supplier or verification service may process sensitive information or initiate actions that affect player accounts.
Security requirements should therefore be defined before development begins.
Key considerations include:
- Secure credential storage and rotation
- Authentication and permission validation
- Encrypted communication
- Input and response validation
- Rate limiting and abuse protection
- Restricted access to production environments
- Logging and monitoring of sensitive actions
- Data minimisation and retention requirements
- Jurisdiction-specific reporting and operational controls
Compliance teams should identify applicable market requirements early. This can prevent expensive rework when an integration is nearly complete but lacks a required control.
Where certification or external approval is required, technical teams should plan the work alongside development and testing. However, an operator cannot guarantee or control the time taken by an external regulator, certification body or provider.
8. Create a Repeatable Integration Delivery Process
Reusable components are most effective when supported by a consistent delivery process.
Without clear ownership, even a technically standardised integration can become delayed by missing documentation, unanswered supplier questions or unclear approval responsibilities.
A repeatable workflow should include the following stages.
Stage 1: Integration discovery
Define the business requirement, provider capabilities, data exchanged, affected platform components and expected operational outcome.
Stage 2: Technical assessment
Review API documentation, authentication, data models, error handling, webhook behaviour, dependencies and provider support arrangements.
Stage 3: Integration design
Select the appropriate adapter, define internal contracts, map data fields and identify security, compliance and reconciliation requirements.
Stage 4: Development
Build the provider-specific connector using reusable platform components wherever possible.
Stage 5: Testing and validation
Run automated tests, sandbox scenarios, contract tests, security checks and reconciliation validation.
Stage 6: Approval and deployment
Obtain the required technical, operational and compliance approvals. Deploy through controlled release procedures.
Stage 7: Monitoring and maintenance
Track integration health, investigate failures, manage API changes and review performance after launch.
Assign one integration owner to coordinate the supplier, engineering, product, operations and compliance workstreams. This reduces delays caused by unclear responsibility.
Maintain an integration playbook containing documentation templates, test cases, approval requirements and deployment checklists. Each completed project should improve the process used for the next one.
How to Measure Integration Efficiency Without Sacrificing Reliability
A shorter development timeline is not necessarily a successful outcome if the integration creates more incidents or manual work after launch.
Operators should evaluate delivery speed alongside quality and operational performance.
Useful measures include:
Metric | What it measures |
|---|---|
Integration lead time | Time from approved requirements to production readiness |
First-pass test rate | Percentage of integrations passing defined tests without major rework |
Defect rate | Issues identified during testing or after deployment |
Webhook failure rate | Percentage of callbacks that fail within the defined delivery process |
Reconciliation exceptions | Number or proportion of records requiring investigation |
Deployment rollback rate | Frequency of releases requiring reversal |
Mean time to recovery | Time required to restore normal integration operation |
Maintenance effort | Engineering time spent supporting existing connections |
Measure these indicators across different integration categories. A game provider connection and a payment gateway integration may have very different testing, approval and operational requirements.
The goal is to reduce avoidable repetition and rework—not to remove necessary controls.
How SwissDice Can Support iGaming Integration Projects
A growing iGaming platform may need to connect game providers, payment gateways and external business systems while keeping existing services stable.
SwissDice can be considered for integration-related technology projects based on the operator's platform architecture, provider requirements and implementation scope.
Relevant areas include:
Games API Integration: Connecting game providers and gaming content through the required API workflows, session handling and platform communication.
Third Party Integration: Connecting external technology services with existing platform components through structured integration workflows.
Payment Gateway Integration: Integrating payment services and transaction workflows into an operator's platform.
The appropriate technical approach depends on the provider's API capabilities, the operator's existing architecture, target markets and required controls. Before starting a project, define the integration scope, testing responsibilities, deployment process and ongoing support expectations.
Conclusion
Reducing integration time is not simply about writing less code or launching a connection faster. It requires a technical foundation that makes integrations repeatable, testable and easier to maintain.
Reusable integration layers, documented API standards, realistic sandbox testing, reliable webhooks, transaction reconciliation and controlled deployments can reduce avoidable development work while protecting platform operations.
For iGaming operators, the most sustainable approach is to treat integrations as a long-term platform capability. Each new provider should build on established standards and components rather than introduce another isolated connection that becomes difficult to support.
With a structured integration strategy, SwissDice can be considered as a technology partner for operators planning new game, third-party and payment integrations while keeping reliability and operational control central to delivery.
Sources & further reading
Sources checked on 2 November 2026. Regulatory examples apply to the named jurisdiction; research forecasts and supplier descriptions retain their own scope.